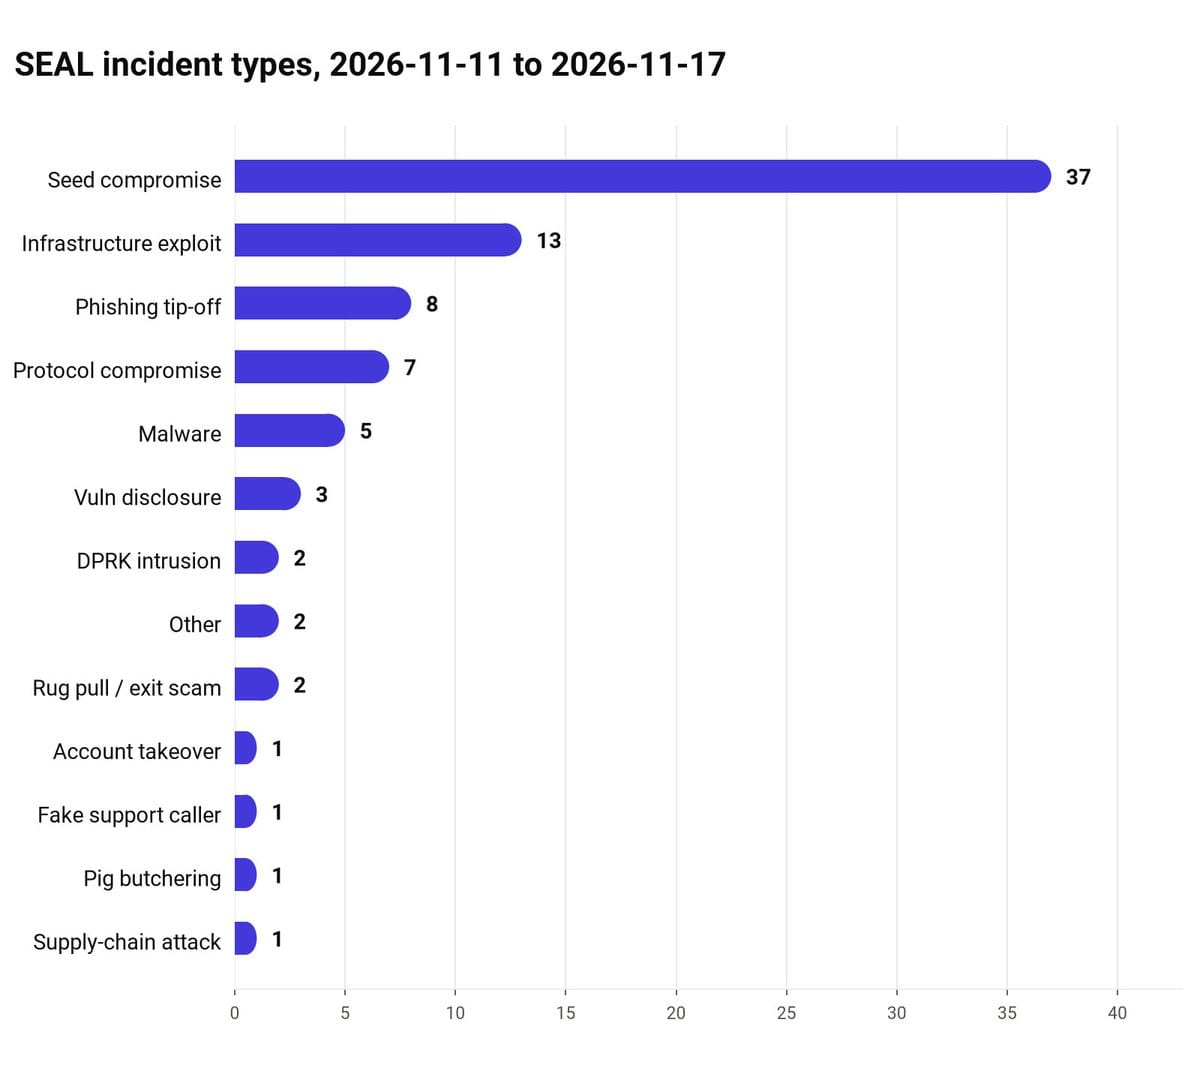
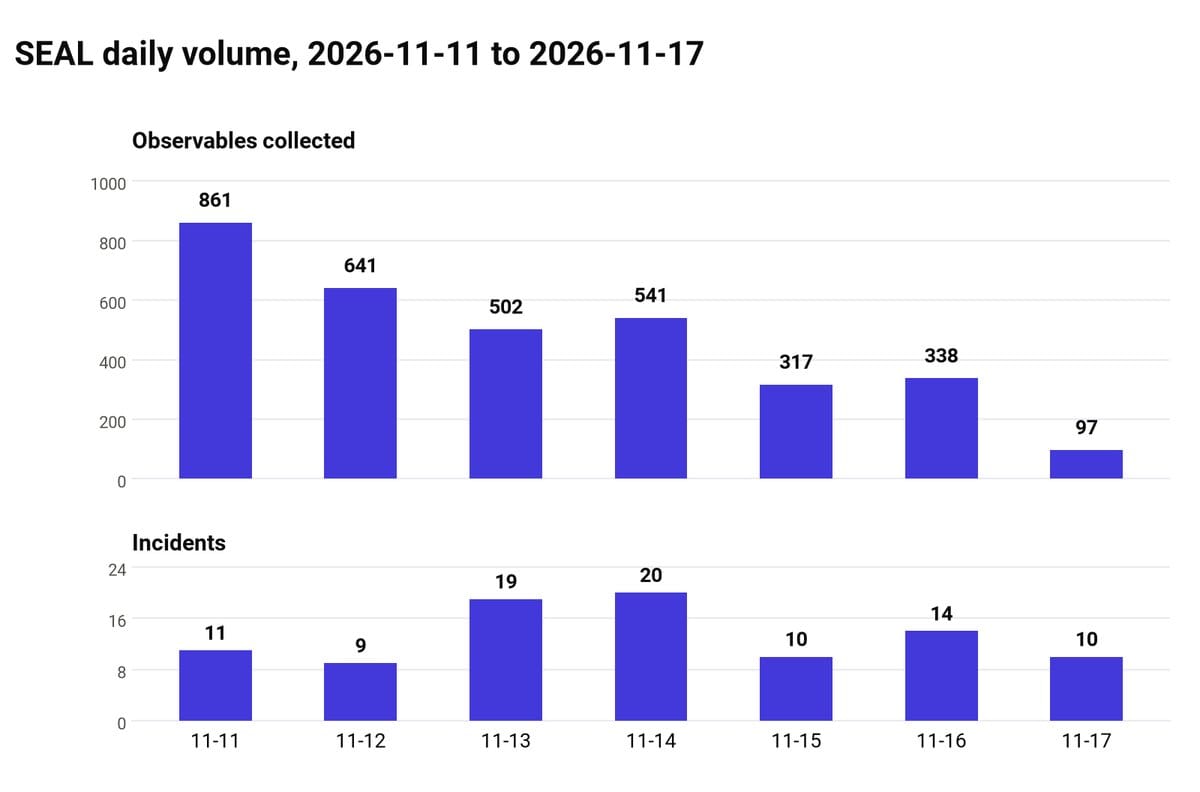
Our team triaged 85 incident reports over the last week. Here are the losses by category:
1) Infrastructure exploit: $23M + 335 SOL
2) Seed compromise: $7.46M + 30.07 ETH
3) Malware: $4.46M
4) Protocol compromise: $1.48M
5) DPRK intrusion: $1.4M
6) Account takeover: $100K
7) Pig butchering: €100K
8) Supply chain: $93K
9) Fake support caller: $67K
What we collected
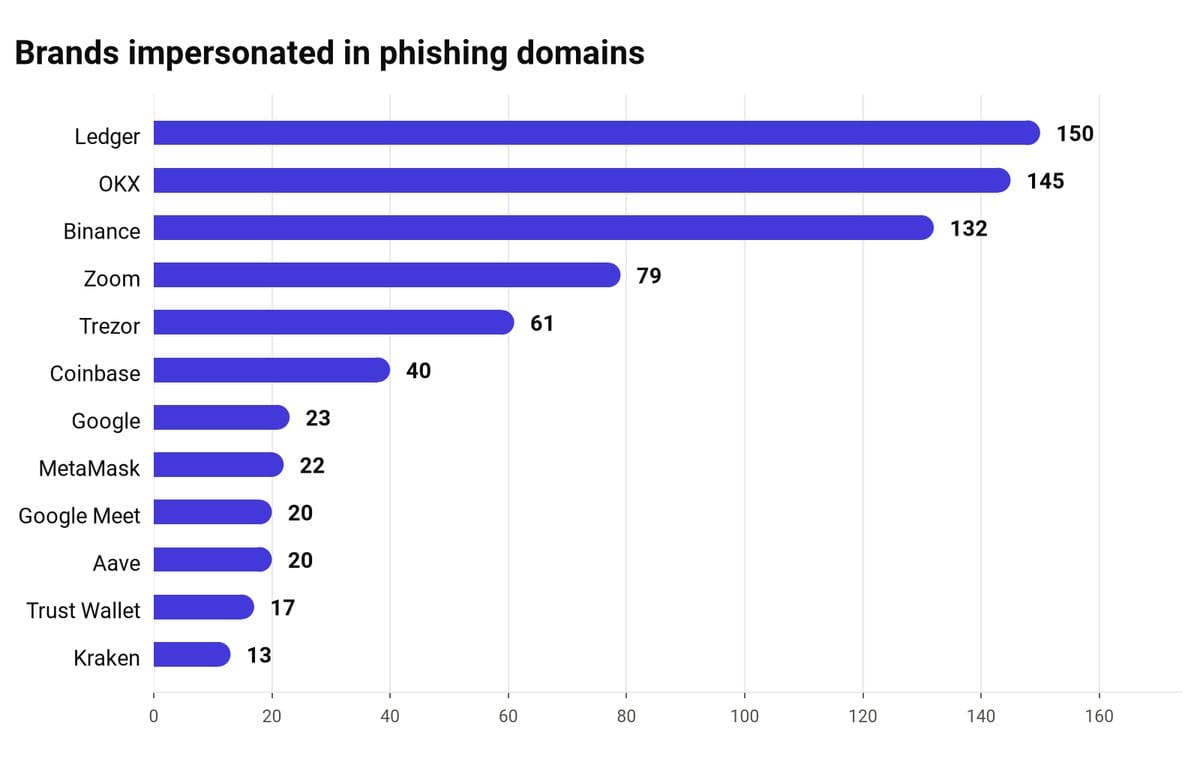
- 3,176 phishing domains
- 3,184 indicators published
- 87 wallets
Protocol Compromise
7 reports = $1.48M reported losses
- ~$1M exploit across three chains.
- $215K from 15 pools through a state-sync function with no access control.
- $200K vault exploit, staking reward-checkpoint bug, & router incident.
And a bridge that minted real tokens for burned fake ones. The project announced a shutdown months ago, but the program is still live and unpatched.
🚨 Unpaused contracts stay exploitable after a project shuts down. Pause or revoke before you walk away.
Infrastructure Exploit
13 reports = $23.03M + 335 SOL reported losses. No contract bug involved in any of them.
- The largest: $17.5M involvding a fund's API key compromised on a trading venue.
- Payment processor lost $3.7M to stolen keys.
- Payment app lost $1.6M to remote code execution.
- Two companies lost funds the same way with an attacker gaining access to their platform, taking the API credential for the custody vault, and the automated co-signer approved every transfer.
🚨 A co-signer that signs whatever your API asks is not a second signature. If you run custody with an automated co-signer: allowlist destinations, cap value per hour, and require a human for anything outside the policy.
Both cases were small simply because the hot vaults were small, but that’s the only control that held.
The Web3Auth key exposure is still producing victims: 5 more reports this week, after 6 last week. Several have staked funds that the attacker's bot will sweep at unbonding.
🚨 If your wallet was created with a Google or Apple login, move what matters to a seed you control.
🚨 A "trade-only" API key isn't safe to hand out. One account lost ~$105K with no withdrawal at all: a third-party app's agent key placed thousands of trades on illiquid markets against a prepared counterparty.
🚨 Revoke agent keys you don’t actively use.
Seed compromise
37 reports = $7.46M + 30.07 ETH reported losses
One wallet accounts for about $6M of it. Most of these victims don’t know how the key left their device, and many wallets hadn’t been used for months while sweeper bots sit on them and take anything that arrives.
iOS wallet compromises
9 reports = ~$184K + 18 ETH reported losses (last week 7, ~$69K).
Trust Wallet, Exodus and others. Suspected DarkSword/Coruna exploit-kit victims.
🚨 Update iOS. Move funds off any seed that lived on an unpatched phone.
🚨 Security alert: we’re still seeing DarkSword targeting crypto wallets on unpatched iPhones.
— 1inch (@1inch) November 17, 2026
Opening a malicious site in Safari can be enough. No wallet connection or signature needed. It goes after private keys and seed phrases.
If you use an iPhone:
▪️ Update iOS now
▪️…
Malware
5 reports = $4.46M reported losses.
- The largest, $4M: a user gave an automated agent access to their keys. How the key was taken is unconfirmed.
🚨 An agent that can sign can be drained. Give it a capped wallet with its own key, never the key that holds your funds.
- ClickFix, $400K. A fake Cloudflare check appeared while the victim was browsing during a call. It asked them to paste a command to prove they were human & that command installed a stealer on a Windows desktop.nexguard[.]pro
🚨 No website needs you to paste a command.
Clipboard hijackers still work. One victim lost ~$48K without any wallet being touched: exchange withdrawals to their own hardware wallet were redirected because malware swapped the address on copy.
DPRK intrusion
2 reports = $1.4M reported losses.
SINT-69 hijacks Telegram accounts and books fake meetings. The FBI attributed it to DPRK (FaceStealer) last week. One victim lost $1.4M to a curl command on a fake Zoom page.
- meetings[.]eu[.]com
- meeting[.]us[.]com
The second DPRK report had no loss: a fake recruiter on LinkedIn --> a Calendly booking --> a "meeting" link on a lookalike domain. It was reported before anything ran.
Contagious Interview
25 new domains this week and we also attributed 36 older job-lure domains to it.
- nodvian[.]us
- invitemeet[.]us
- yorameet[.]us
- anymeetex[.]com
- anymeethub[.]com
- cloudmeetly[.]org
- corviameet[.]us
- elviameet[.]us
- gomeetbridge[.]com
- meethubly[.]com
- oviameet[.]com
- talomeet[.]usalpha-sense[.]app
- alphasense[.]app
- alphasights[.]eu
- alphasights[.]us
- glginsights[.]org
- cortiva[.]us
- gotvio[.]com
- introvisto[.]us
- noventrax[.]us
- syncmorrow[.]us
- talkbrave[.]app
- viresto[.]us
Fake meeting pages, currently unattributed:
- microosoft-teams[.]com
- microsof-teans[.]com
- microsoft-teans[.]com
- microsot-teams[.]com
- teams-micrsoft[.]com
- microsot-team[.]com
- zoomworkplaces[.]com
- us14zoom[.]us[.]com
- us15zoom[.]us[.]com
- joinmeetscall[.]online
Fake podcast invites:
- streamyard[.]me
- streamyard[.]site
- streamyard[.]watch
- slack-huddle[.]com
- huddle-slack[.]com
Our incident response service is free to anyone who needs it, and stays that way because people from the community fund it.If this week's numbers are useful to you, fund the next one: https://securityalliance.org/donate
If you require a direct data feed from SEAL-ISAC, contact us at [email protected].