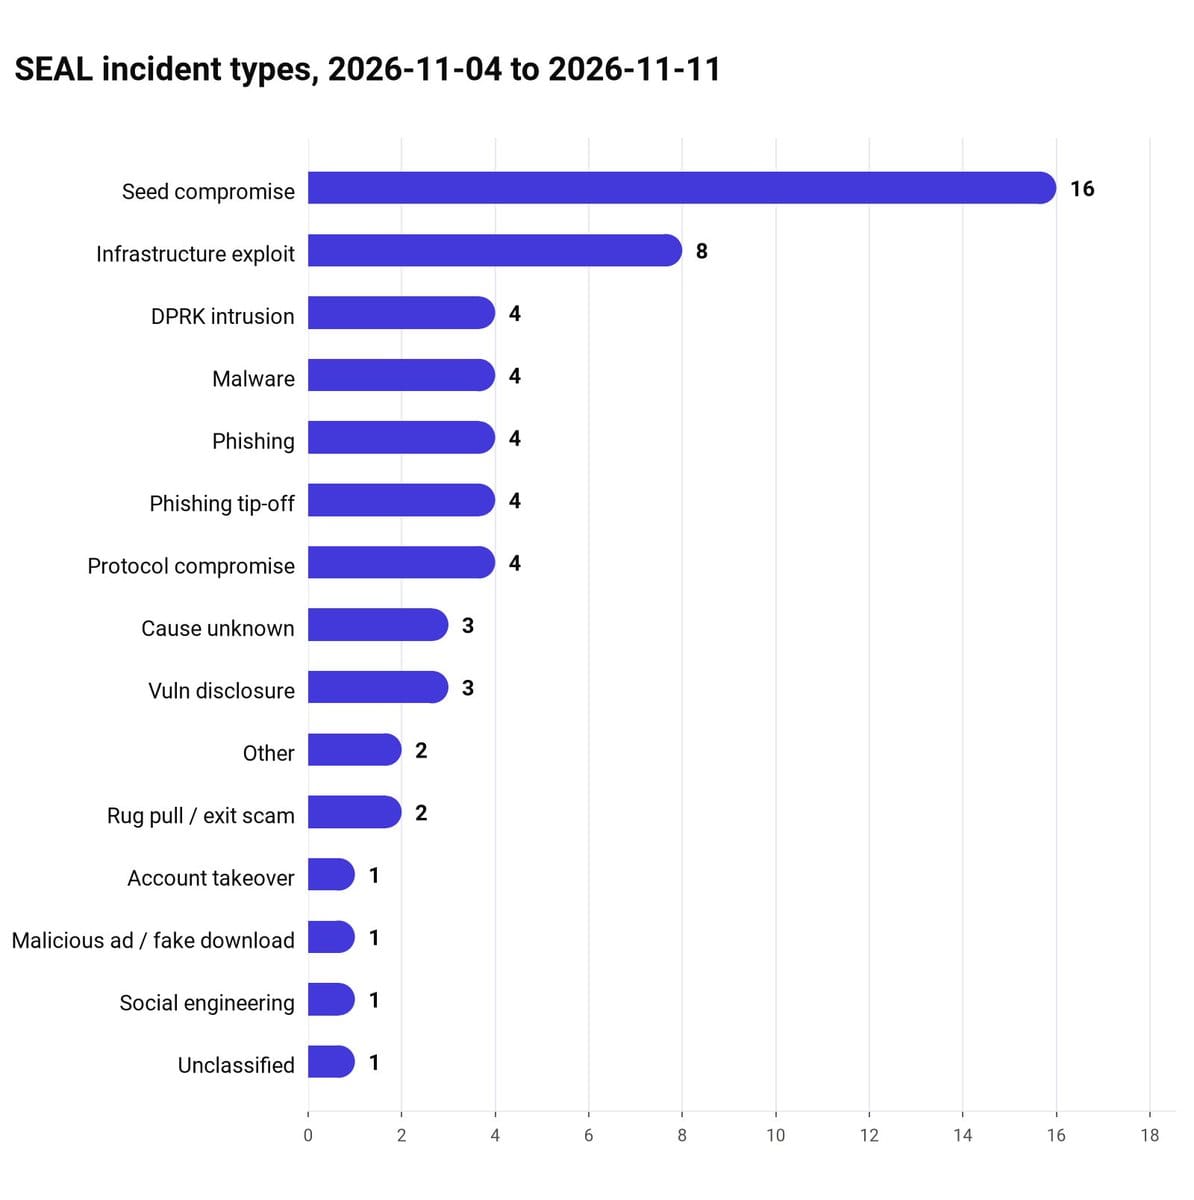
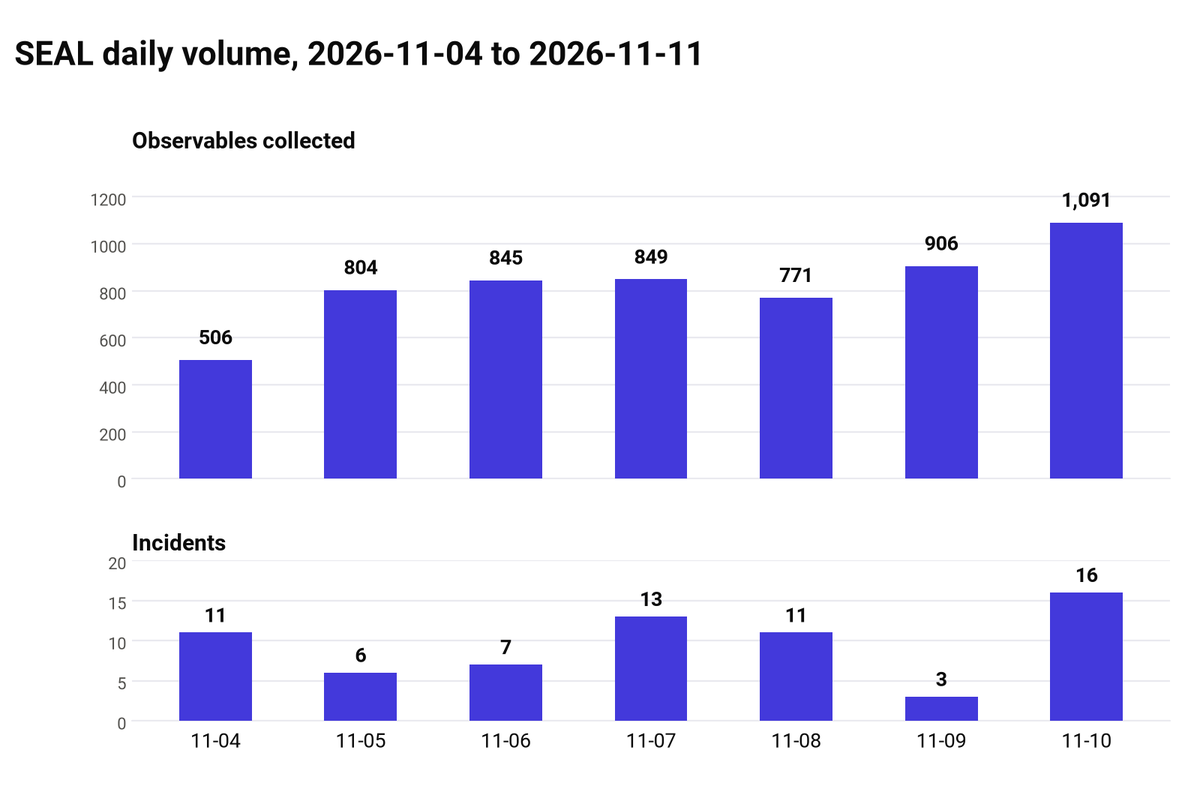
This past week, we triaged 60 incidents. In this post, we share losses by threat category, what we collected, and IOCs.
Losses by category
1) Protocol compromise: $3.87M
2) Social engineering: €3M
3) Infrastructure exploit: $914K
4) Phishing: $623K
5) Seed compromise: $169K
6) Malware: $108K
7) DPRK intrusion: $35K
What we collected
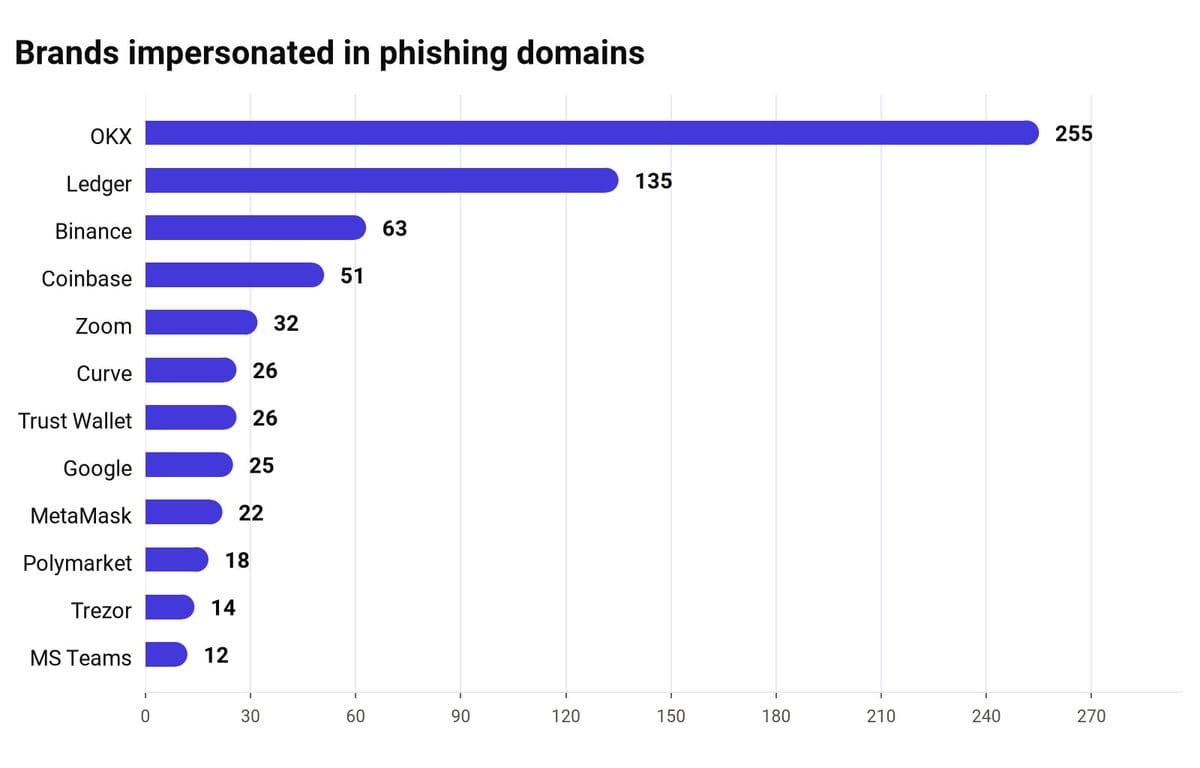
- 5,640 phishing domains
- 5,652 indicators published
- 105 wallets
Protocol Compromise
4 reports for a total $3.87M loss:
- $2.2M exploit
- $1M Loopscale
- $665K exploit
- ~$200K concentrated-liquidity exploit
Infrastructure Exploit
8 reports including: bridge DNS hijack, compromised servers, and hosted drain.
We continue to see heavily automated attacks run by attacker-controlled LLMs focused on gaining the smallest possible foothold into the many services and dependencies that Web3 protocols and operators rely on.
Registrar DNS hijacks continue with a suspected root cause of social-engineering against registrar support staff. In fact, a bridge front-end's DNS was hijacked just yesterday. In every case we observe, the final payload is a custom crypto drainer aimed at users' wallets.
For protocol operators, we recommend: registry lock, 2FA at the registrar, and monitoring of your NS records. Check out our Framework on registrar security & registry locks: https://frameworks.securityalliance.org/infrastructure/domain-and-dns-security/registrar-and-locks
🚨 If you get hijacked, open a ticket with SEAL immediately. We can help with incident response and temporary domain blocking.
DPRK
4 reports this week with only $35K loss confirmed:
- UNC1069 fake Teams invites
- Contagious Interview fake job (stopped halfway through npm install)
- $35K PolinRider victim
- Researcher intel on a job-lure cluster running on the OverlordRAT platform
The classic Contagious Interview campaigns are still ongoing. The interview repo's .vscode/tasks.json ran wget | sh on open. Stage 1 pulled a bootstrap from a Vercel host, stage 2 set persistence, stage 3 was obfuscated JS calling a bare IP on port 1224.
evmrpc-testnet-0g[.]vercel[.]app
Read .vscode before opening a stranger's repo. Check out our previous blog post on DPRK's use of VS code task for more details: https://radar.securityalliance.org/vs-code-tasks-abuse-by-contagious-interview-dprk/
New DPRK UNC1069 infrastructure
5 domains + Teams lookalikes again:
- taennslieve[.]com
- teennslieves[.]com
- teamslive[.]co
- teams06live[.]us[.]com
- meet-in[.]store
Suspected, not confirmed:
- us05cloud[.]online
- us06cloud[.]online
The job-lure cluster, UNK_DeadDrop (Proofpoint's designation), is a close sibling of Contagious Interview run by different DPRK operators. It uses an open-source C2 panel (Overlord RAT, ~44 panels under affiliate brands), ~98 recruitment-lure domains on one bulletproof host, and a single mass-mailing service that blasts fake job offers to addresses scraped from public sources such as GitHub.While classic Contagious Interview campaigns usually utilize LinkedIn cold outreach and delivery of malicious repositories, UNK_DeadDrop is being delivered directly to email inboxes and ends up with a "verification" ClickFix command at the end of job application form user is asked to fill in.
SINT-69
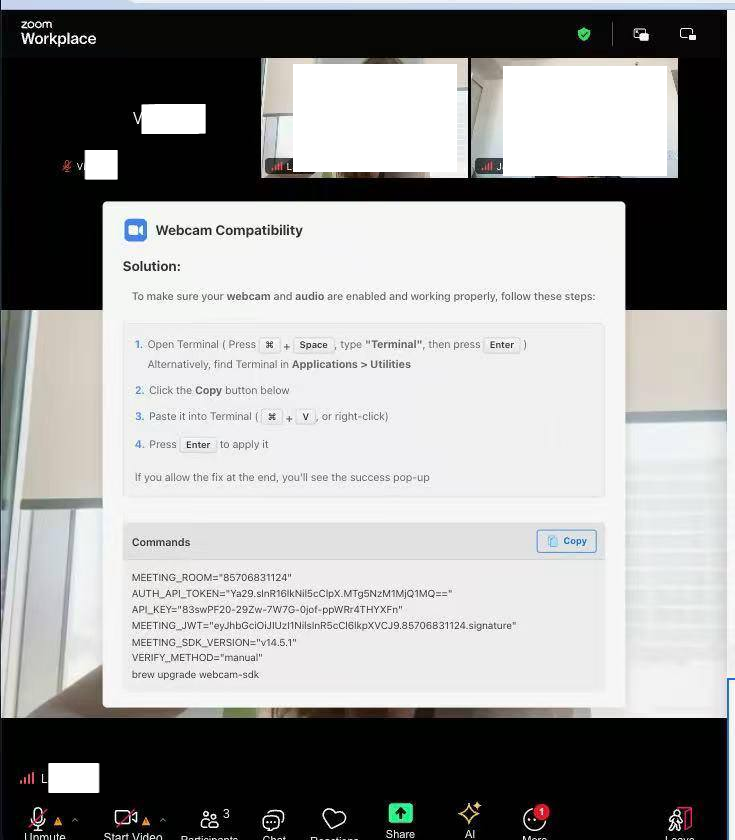
This is an uncategorized intrusion set that hijacks Telegram accounts and books fake meetings (closely following DPRK UNC1069 TTPs). One $90K loss this week from a compromised contact asked for a catch-up, then the fake Teams page asked the victim to paste a command and this individual stopped at the password prompt, after stage one had already run.
IOCs:
- neoramo[.]com (ClickFix payload host)
- teamicrosft[.]us[.]com (Phishing front end)
Fake job interviews on Windows
A "Saifuro LLC" recruiter + a meeting link that required a "Vettasy Launcher" MSI. It dropped two Python backdoors and a hidden Chrome profile for cookie theft. One victim lost $17K and one caught it at install. We've seen multiple public reports describe other victims.
"Vettasy" and similar video-conferencing platforms are attacker-controlled and used to deliver the initial malware payload. Don't take meetings on platforms you don't recognize, or on any platform that requires you to download unknown software.
saifuro[.]com
vettasy[.]com
vettasy[.]com/join/K7M4-Q2RD
infos.updates[.]com[.]co
172.67.170[.]200
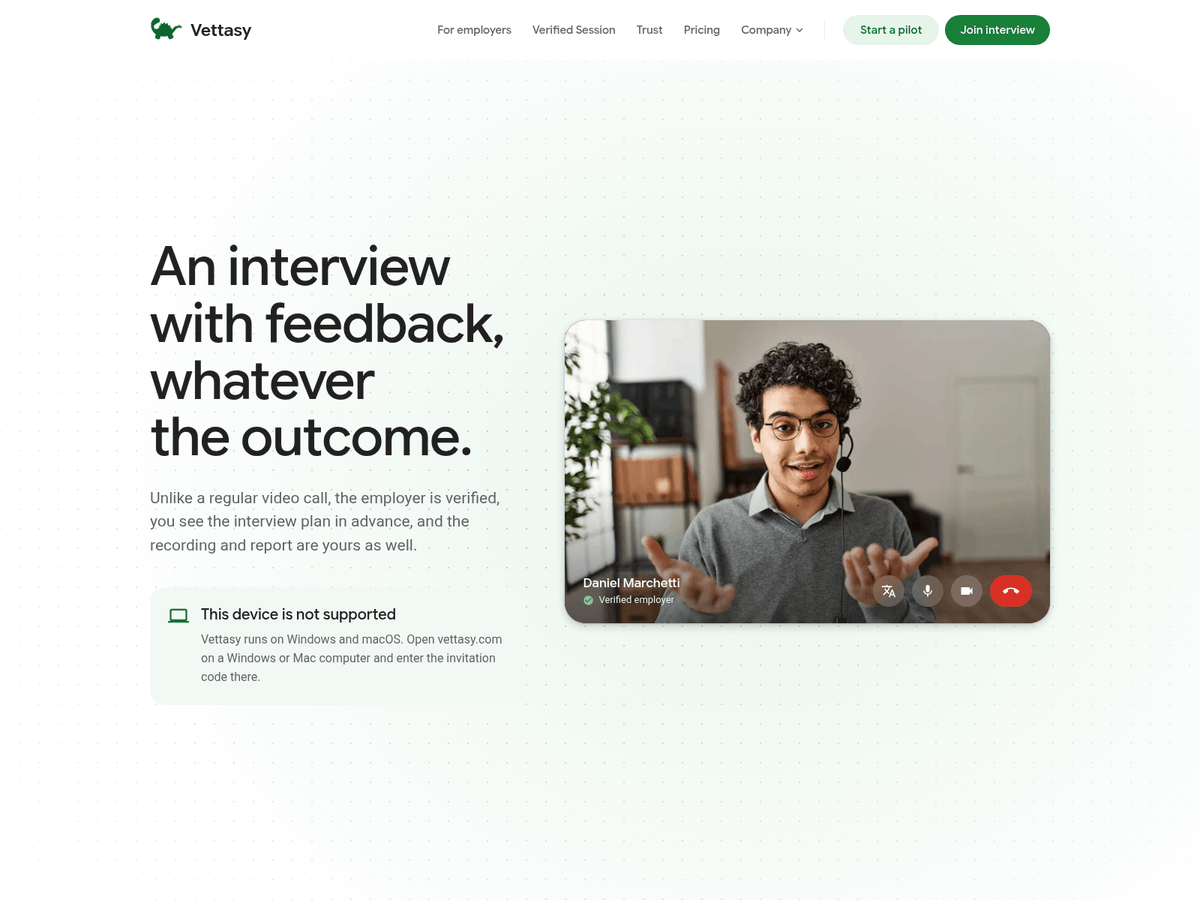
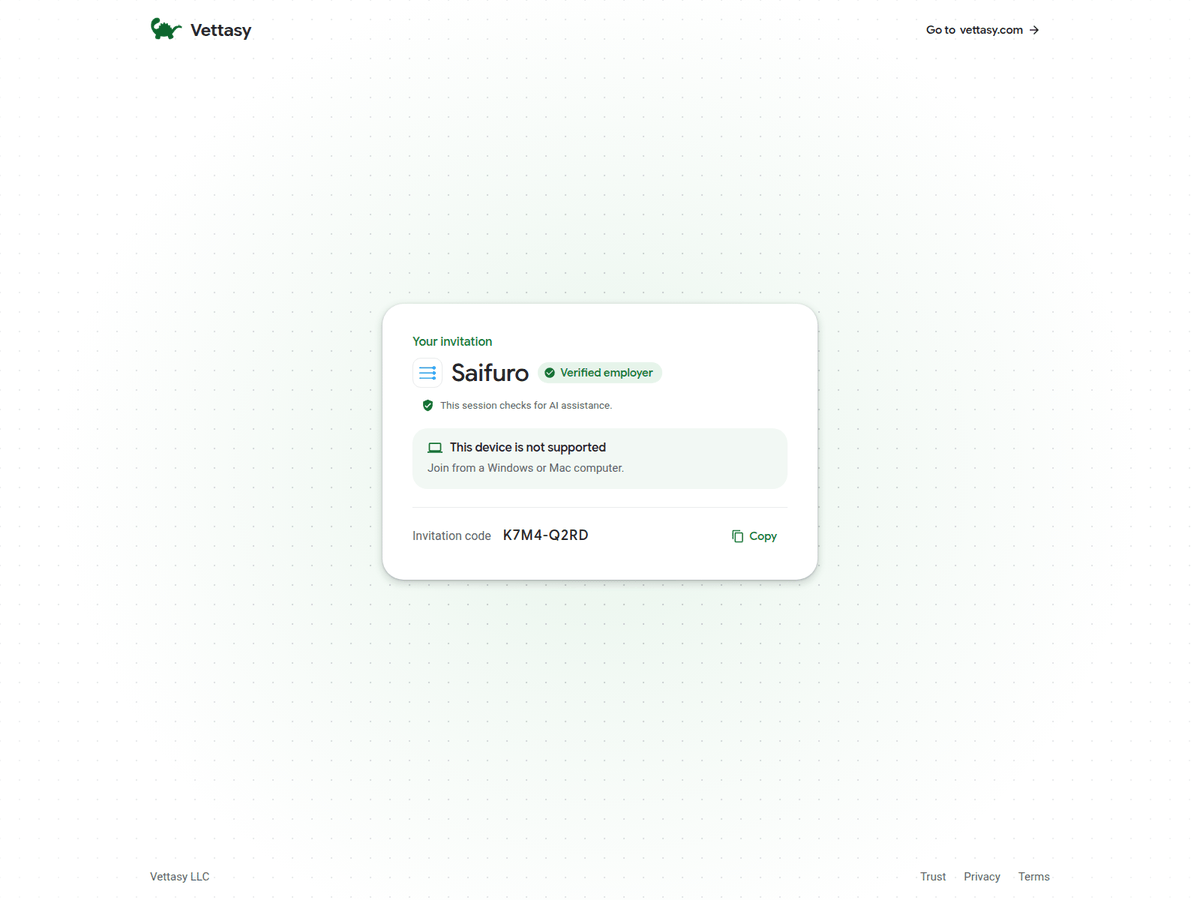
Fake meeting and ClickFix pages
Unattributed, 13 new:
- us01-zoom[.]cc
- us02-zoom[.]cc
- us05web-zoom[.]club
- us12zoom[.]us[.]com
- ux05webzoom[.]com
- ue05webzoom[.]com
- ur05webzoom[.]com
- joinwebexmeeting[.]us
- com-join[.]us
- meets-room[.]live
- mymeet[.]cc
- calls-us[.]online
- fileharbor[.]net
iOS wallet compromises
We received 7 reports, totally ~$69K in losses (for comparison: last week 6 report, ~$127K lost), including Trust Wallet and others using a suspected DarkSword/Coruna exploit-kit. One victim discovered the loss 46 days after the fact.
🚨 Suspected, not confirmed with our victims. Update iOS now!
The malware is usually delivered through sub-resources loaded by otherwise benign pages. This is a zero-click exploitation, needing no interaction from the user.
Seed Compromise
- 16 reports: $169K
Phishing
- 4 reports, $623k:
- $535K to a fake QR code
- $55K via a malicious conference link
- 27K "bookmark" scam
- $60K fake Ledger Google ad
The largest single loss of the week is not an exploit, but an issuer's wallet drained of about €3M, after multi-stage social engineering during a high-value asset transfer between companies.
A Solana trading bot's wallet was drained of ~$856K. Root cause undetermined.
Our incident response service is free to anyone who needs it, and stays that way because people from the community fund it.If this week's numbers are useful to you, fund the next one: https://securityalliance.org/donate
If you require a direct data feed from SEAL-ISAC, contact us at our website: securityalliance.org.