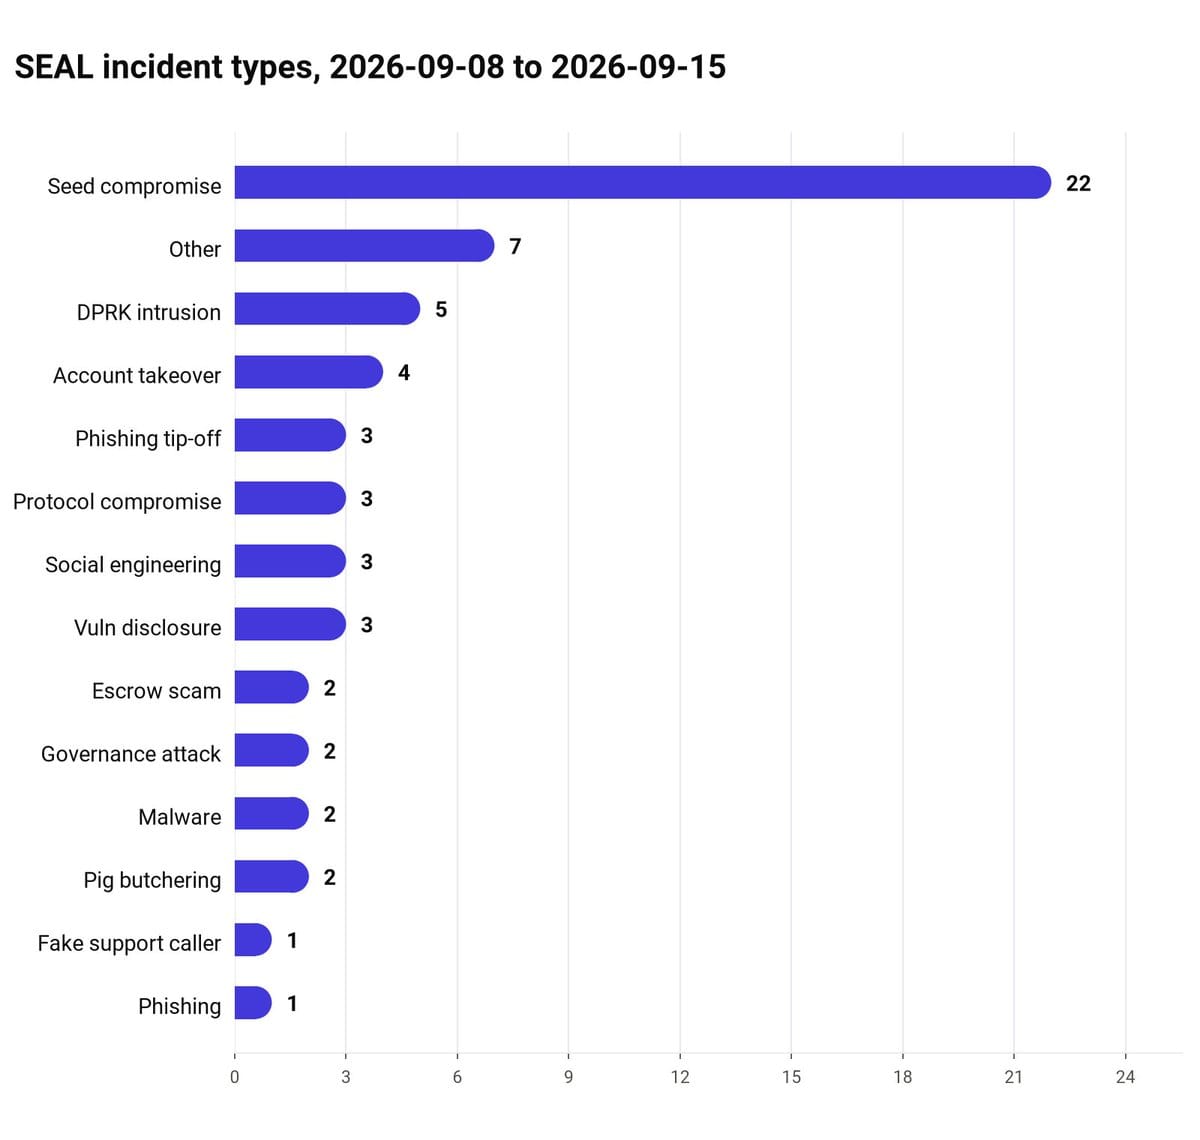
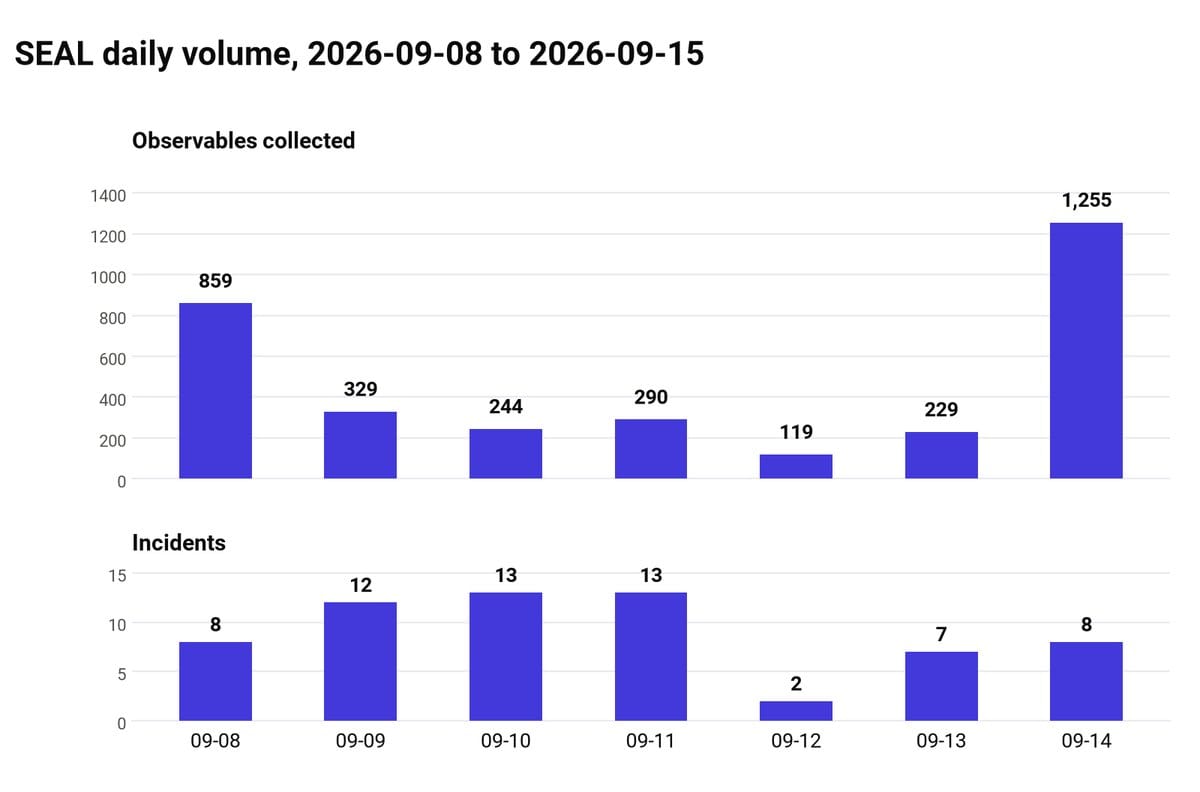
This week, our team dealt with 61 incidents and 17 of them involved compromised seed phrases or private keys. Root causes typically include a compromised device, re-typing the seed into a fake wallet app, or exposing the seed to third-party storage. The largest loss was $5.4M due to a seed kept in cloud storage.
Here are the reported losses of the incidents we dealt with by category:
- Seed compromise: $9.39M
- Protocol compromise: $3.94M
- DPRK intrusion: $2.9M
- Escrow scam: $1.68M
- Malware: $960k
- Social engineering: $192k
Plus 132.5 ETH lost - distributed across all categories.
What we collected
- 3,192 phishing domains
- 3,226 indicators published
- 74 wallets
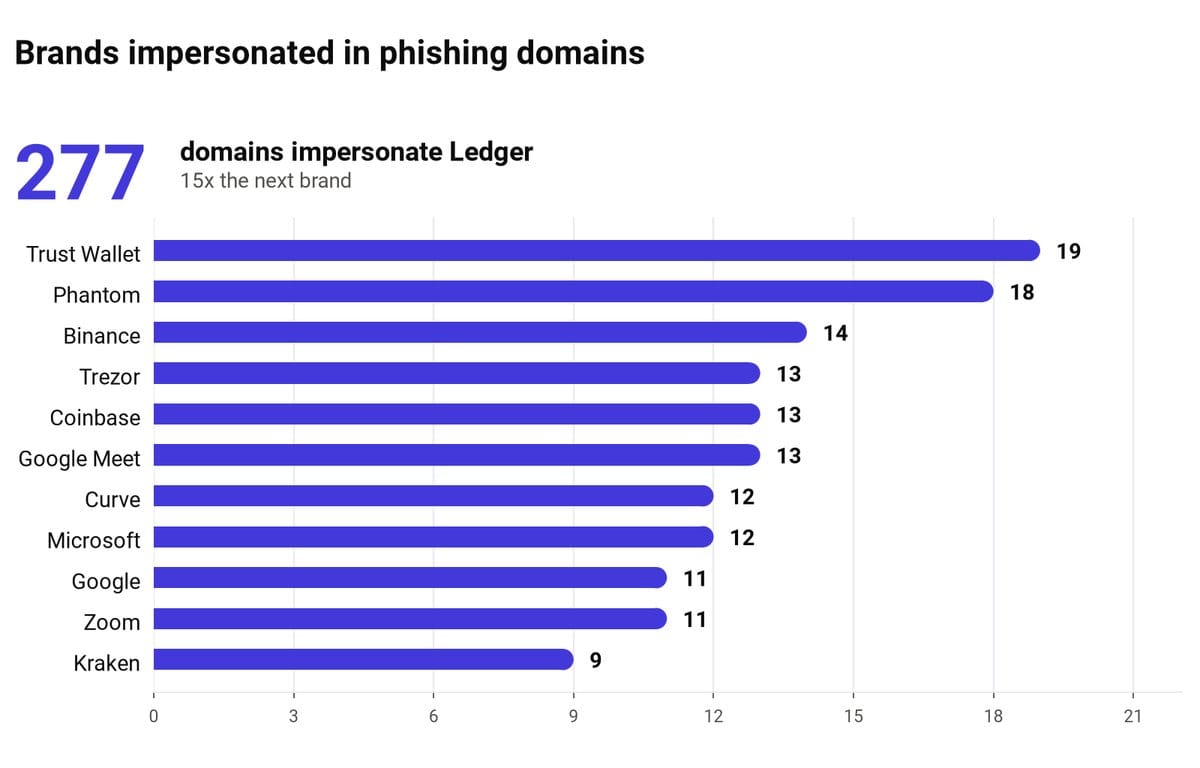
Ledger was impersonated 277 times compared to last week's 29 and 15x the next brand.
DPRK
- Contagious Interview: $1.9M
- IT worker hired onto the team: $500k
- SINT-01 (Konni): $480k
All three successful intrusions occurred months before the theft. DPRK actors persisted on developers' devices and infrastructure for an extended period. In the case of the DPRK IT worker, an insider leveraged his access to critical infrastructure and withdrew funds to his wallet.
We engaged on a single incident involving UNC1069 with $0 loss.
IOCs
- texmslives[.]com
- tezmlives[.]com
- tevmslives[.]com
- microteamscall[.]com
- usonliues[.]us
- 365lineup[.]com
This week's outlier involves fake wallet apps distributing Android APKs targeting Chinese users. In one case we tracked the user lost to ~$1M.
- tronlinkwallet[.]cn
- trustwallet-web3[.]cn
- ledgerwallet-app[.]cn
- imtoken-web3[.]cn
- tokenpocket-web3[.]com[.]cn
- binancewallet[.]com[.]cn
Unattributed fake meeting campaigns:
- gogglemeets[.]com
- us04-web-zoom[.]us
- workspace-zoommeeting[.]us
- meetinglinvite[.]com
- zoom[.]com[.]im
Our incident response service is free to anyone who needs it, and stays that way because people from the community fund it.If this week's numbers are useful to you, fund the next one: https://securityalliance.org/donate
If you require a direct data feed from SEAL-ISAC, contact us at [email protected].